Penetration testing, code audits & AI slop cleanup
We try to break into your system before someone else does, and clean up sloppy AI code.
Initial security and code checkups are free unless we find issues above low severity. We charge for real fixes and code cleaned.
Real examples
How checkups and cleanup work
Pick the target
Point us to the app, server, API, or codebase you want checked for security holes or AI code slop.
Free initial checkup
We lock down written bounds and run the initial review. If we find only items of low severity or recommendations, you pay nothing.
Report on real findings
When our AI agents and engineers uncover medium+ holes or heavy code slop, a small success fee unlocks the full report with proof and fixes.
Pay per fix & code cleaned
Need us to patch the holes or strip out the slop? We charge by the actual issues fixed and code lines cleaned, not mystery hours.
What we test
Web and mobile apps, APIs, Linux servers, internal networks, Java/.NET backends, and source code, using Burp Suite, Gobuster, and our own tooling. In codebases, we also strip out AI code slop: dead abstractions, duplicated logic, and fragile tangles.
What it costs
Initial checkup is free on both security and code reviews unless we find issues above low severity or recommendations. A small success fee then unlocks the full report, and we charge strictly by actual issues fixed and code lines cleaned, not unexplained work.
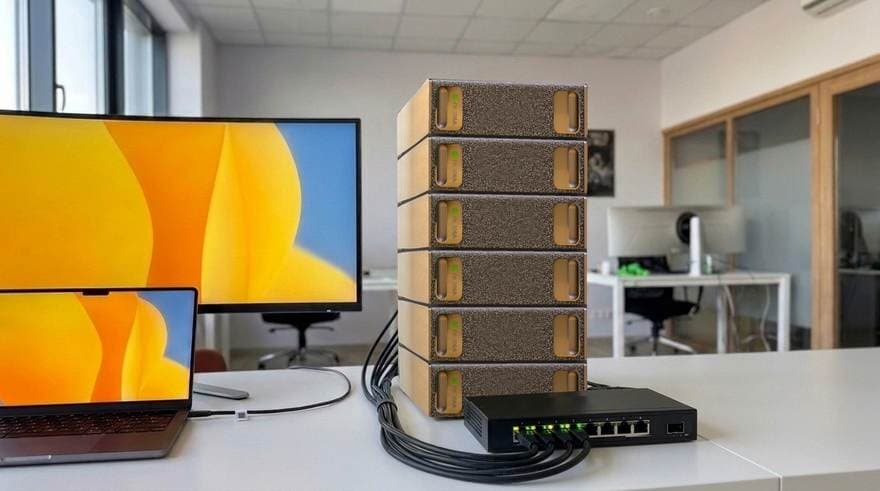
Your documents, data, and code stay private.
We run security tests and code audits on our 6 × NVIDIA DGX Spark rack in Vilnius using local models near Opus 5.5. Your code and data never leave the rack.